Upvotes
0
Pricing
Open Source
Category
Prompt Generators
In the database since
Oct 2026
Overview
About Promptfoo
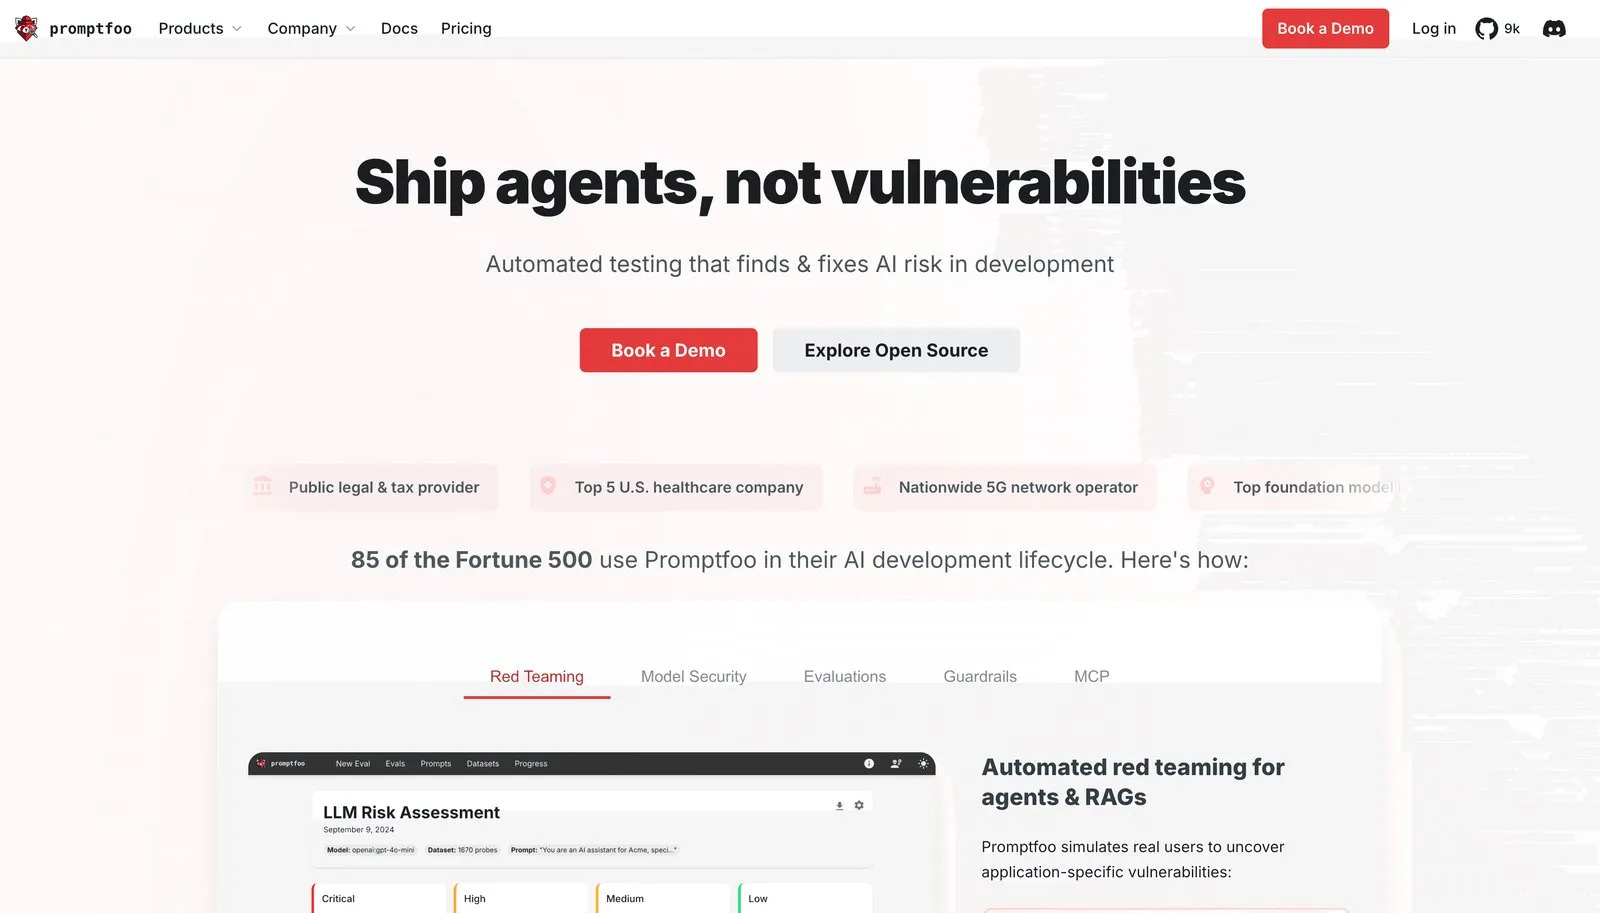
Promptfoo is an open-source toolkit for testing and securing AI applications before they reach users. It runs automated evaluations on your prompts, models, and RAG pipelines, and it red-teams them by simulating attacks like prompt injections and jailbreaks. Developers run it from the command line or plug it into CI/CD pipelines. The project is MIT licensed and stays open source even after joining OpenAI. Its docs and GitHub repo are the best place to check current setup steps. It is built for teams shipping AI features to production.
Key Features
1. Automated Prompt Evaluations
Define test cases in a config file and Promptfoo scores your prompts and models against them, so regressions show up before release.
2. Agentic Red Teaming
It generates thousands of context-aware attacks for your app, including prompt injections, jailbreaks, PII leaks, and insecure tool use.
3. Side-by-Side Model Comparison
Run the same tests across OpenAI, Anthropic, Bedrock, Ollama, and more to compare quality, cost, and safety in one view.
4. CI/CD Integration
Hook evaluations into GitHub Actions, GitLab, or Jenkins so every pull request gets checked for prompt and security regressions automatically.
5. Code Scanning
It reviews pull requests for LLM-related security and compliance issues and suggests fixes right inside your developer workflow.
6. Guardrails and MCP Proxy
Beyond testing, Promptfoo offers real-time protection against jailbreaks plus a secure proxy for Model Context Protocol traffic.
Frequently Asked Questions (FAQ)
How do I install and run Promptfoo?
Install it with npm, Homebrew, or pip, or run it without installing via npx promptfoo@latest. You write a small YAML config with your prompts and test cases, then run promptfoo eval. Results open in a local web viewer where you can inspect every output.
What does red teaming actually test?
Red teaming simulates an attacker probing your AI app. Promptfoo generates custom attacks for your target: direct and indirect prompt injections, jailbreaks tuned to your guardrails, data and PII leaks, business rule violations, and toxic content. Each finding comes with remediation guidance.
Do I need my own API keys to use it?
Yes. Promptfoo does not bundle model access, so you set API keys for your chosen providers as environment variables. This keeps your usage on your own accounts and lets you test any provider you already pay for, from OpenAI to local Ollama models.
Is Promptfoo still open source after joining OpenAI?
Yes. The GitHub README states Promptfoo is now part of OpenAI and remains open source under the MIT license. The CLI, library, and docs continue to be developed in the open, and the community of over 300,000 developers keeps contributing.
How is this different from a prompt playground?
A playground is for trying one prompt by hand. Promptfoo is for systematic testing: versioned test suites, dataset-driven evals, regression tracking, and security scans that run automatically. It fits teams shipping AI features who need proof their prompts behave, not just a chat box.
Conclusion
Promptfoo suits developers and AI teams who need more than vibes to trust their prompts. Its evals catch regressions, its red teaming finds security holes, and the open-source license means you can self-host everything. If you ship LLM features to real users, testing them with Promptfoo is a sensible step before launch. It works with the models you already use.
Keep exploring
Similar AI tools
Ranked by the job they do, their capabilities, and how closely they fit this workflow.